"Inside the Mind of a Hacker : The Professional 'Kill Chain' Process"
"To be effective, a Pentest must follow a well-defined plan. This ensures that every corner is checked while maintaining system availability—meaning your business operations stay up and running. Generally, there are five key steps involved:"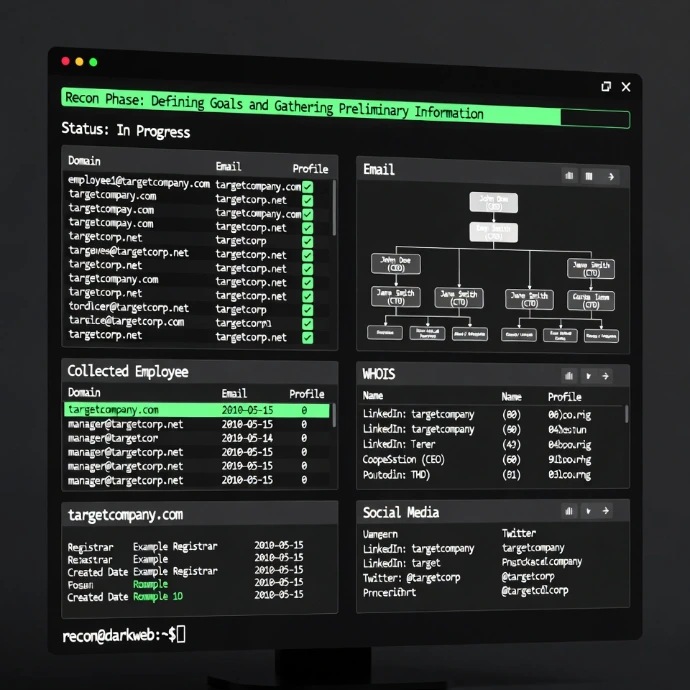
Planning & Reconnaissance
Defining goals and gathering preliminary information (e.g., domain names, employee emails)
Scanning
Scanning: Using tools to identify open ports and detect any misconfigured or abnormal services..
Gaining Access
This is where testers will start exploiting vulnerabilities they find (e.g., SQL Injection or Broken Authentication) to gain access to the system.
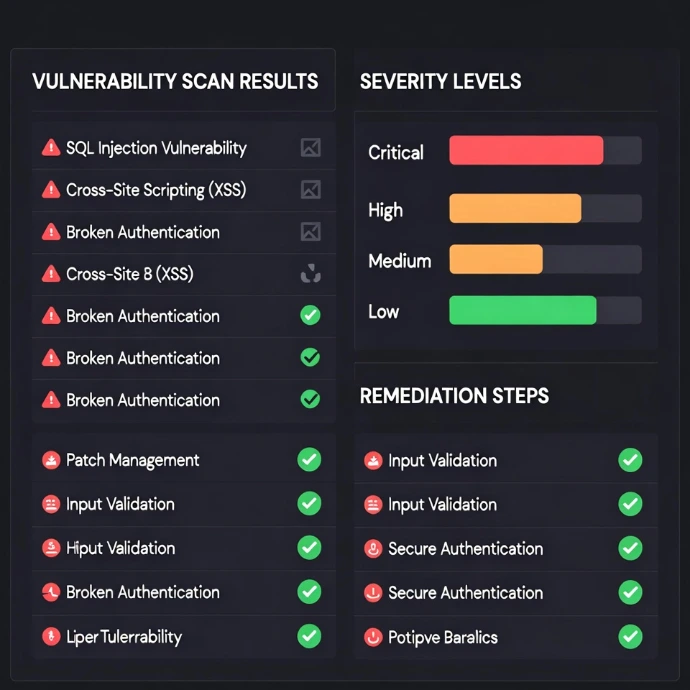
Analysis & Reporting
The most critical phase involves summarizing the findings, their severity levels, and providing 'remediation' or a clear roadmap for how to fix them."
Maintaining Access
Determining how long they can stay 'embedded' without being detected—mimicking hackers who remain hidden until they are ready to deploy ransomware"Why is Pentesting the 'Vaccine' for Modern Businesses?"
If you are still hesitant about whether to perform a Pentest, consider these reasons:
Incalculable Damage: The cost of a Pentest—typically in the hundreds of thousands—could prevent millions in damages from ransomware or heavy fines under PDPA laws if customer data is leaked.
Compliance & Trust: Many international standards, such as PCI-DSS (for credit card businesses) or ISO 27001, mandate regular Pentesting. Furthermore, it helps build confidence among business partners and investors.
Finding Logical Flaws (Human insight vs. Bot detection): Automated programs might miss a bug on your checkout page that allows someone to change a product's price to 1 Baht. However, a Pentester will specifically test for these logic flaws.
Common Misconceptions about Pentesting
As experts at Cybernetics Plus, we frequently encounter these questions and would like to share the answers:
"Is it a one-time thing?": The answer is no. Software systems are constantly updated, and new vulnerabilities (Zero-day) emerge every day. We recommend performing a Pentest at least once a year or whenever there is a major change in your system architecture.
"Will a Pentest crash my system?": If conducted by professionals with a clear Rules of Engagement (RoE), the risk of a system crash is extremely low. Testers focus on proving the existence of vulnerabilities rather than causing destruction.
"We already have a firewall, so we don't need it": A firewall is like a security guard at your front gate, but hackers might enter through the "sewage pipes" or "ventilation ducts." A Pentest reveals exactly where those hidden openings are.
"Penetration Testing is not a sign of weakness; rather, it demonstrates an organization’s 'Security Maturity.' Knowing your own vulnerabilities before someone else does is the key to staying one step ahead of cybercriminals.
If your organization handles online transactions, stores customer data, or utilizes cloud systems, a cyber health check through Pentesting is no longer a 'nice-to-have'—it is a 'must-have' in the era of Digital Transformation."
IT Health Check : Identify Vulnerabilities and Seal Leaks Before Damage Occurs
“Investing thousands in prevention is better than spending millions on recovery.” Gain total confidence in your system security with our Vulnerability Assessment (VA Scan)—accurate, fast, and compliant with international standards.

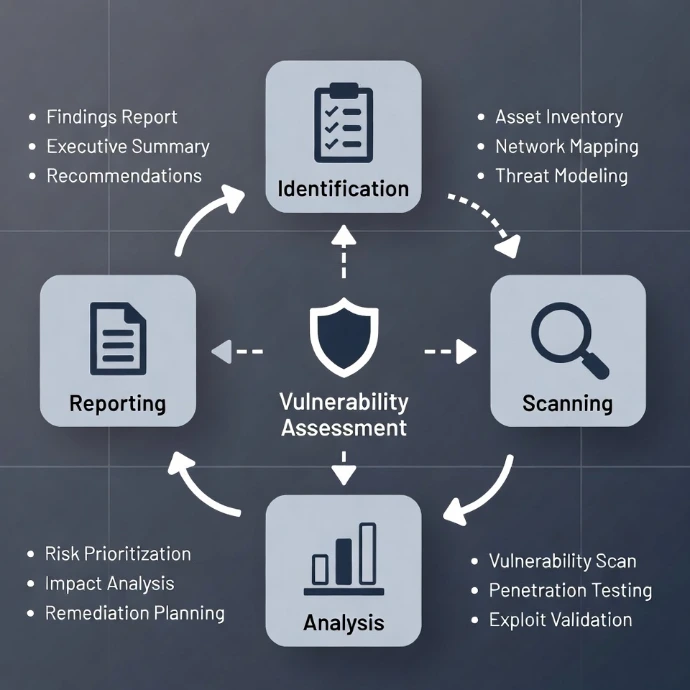
What is a VA Scan?
What is a VA Scan and why does your business need it?
If your IT system is your "home," a VA Scan is like hiring a professional inspection team to check every corner. Are the door locks loose? Is a window left unlatched? Is there a gap in the fence large enough for a burglar to climb through?
Vulnerability Assessment (VA Scan) is a process that utilizes intelligent tools integrated with AI to scan for weaknesses in your network, servers, or software. It allows you to "know first" before a hacker does, giving you the time to close those gaps effectively.
VA Scan vs Pentest
Choose the Right Path: A General Check-up or Targeted Surgery?
Many organizations are unsure which service they need. Here is a simple breakdown
Comparison | VA Scan (Annual Health Check) | Pentest (Targeted Surgery) |
Method | Focuses on broad coverage; identifies overall weaknesses. | Focuses on depth; simulates real hacking to access data. |
Speed | Fast; provides quick results and summaries. | Time-consuming; requires high-level expert skills. |
Frequency | Can be done frequently (Monthly / Quarterly). | Recommended after major system changes (Annually). |
Budget | Affordable; ideal for SMEs. | Higher cost; varies by target complexity. |
VA Scan (Vulnerability Assessment): Think of this as an "Annual Physical Exam." We use specialized tools to scan for weaknesses across the entire body (system) from head to toe to identify any potential risks of serious illness. It is comprehensive, budget-friendly, and can be performed frequently.
Pentest (Penetration Testing): This is like "Targeted Surgery." It is a simulation of a real-world hacker attack to see exactly how well your fortresses hold up under pressure. (This is highly recommended after you have already sealed the gaps found during the VA Scan).
3 Core Pillars of a VA Scan

Identify (Find the Gaps)
Exactly where are the weaknesses hiding within your system?

Classify (Prioritize Risks)
Which vulnerabilities are "Critical" (Red) or "Low Risk" (Green)? This allows you to focus your resources on fixing the most vital issues first.

Why Choose Us?
We utilize global-standard scanning tools integrated with AI Analytics to filter data and reduce False Positives, ensuring you receive accurate, actionable insights.
Our reports are designed to meet ISO 27001 and NIST standards, while fully satisfying PDPA legal requirements.
Our scans are meticulously configured to ensure they do not impact your core operations. Your business keeps running smoothly without interruption.
5 Steps to Seamless System Security
Scoping & Strategy
We meet to define the scope (IPs / Domains) to ensure maximum precision.
Deep Scanning
We perform a deep-dive scan to find vulnerabilities in OS, software, and misconfigurations.
Analysis & Verification
We perform a deep-dive scan to find vulnerabilities in OS, software, and misconfigurations.
Final Reporting
We deliver an Executive Summary and a Step-by-Step Technical Guide for remediation.
Re-scanning (Follow-up)
The most vital step. After you apply the fixes, we scan again to confirm that the leaks are truly sealed.
Cybersecurity Awareness Training
Transform Your "Weakest Link" into Your "Strongest Defense."
Because 95% of cyber threats stem from Human Error. Elevate your organization's security with Cybersecurity Awareness Training from Cybernetics+.
Protect your corporate data before it’s too late.

Technology Protects Your Systems, But Who Protects Your "People"?
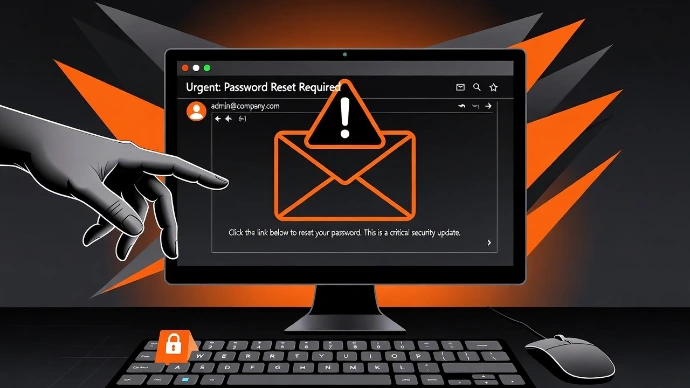
Phishing Attacks
Deceptive emails are becoming indistinguishable from real ones. Can your employees spot the difference?
Ransomware
A single click can lock down your entire company’s files and lead to costly extortion.
Weak Passwords
Easy-to-guess passwords are the "master keys" hackers love the most.
Fact Check: "Did you know? Most organizations spend a fortune on technical Firewalls but neglect investing in the Human Firewall."
Cybersecurity Awareness Training by Cybernetics+
We don't just "teach"; we build a "Security Culture" through a modern, measurable process.
The Solution
Interactive Learning
Engaging, non-boring interactive modules that are easy to understand. Perfect for all levels (Non-IT Friendly).
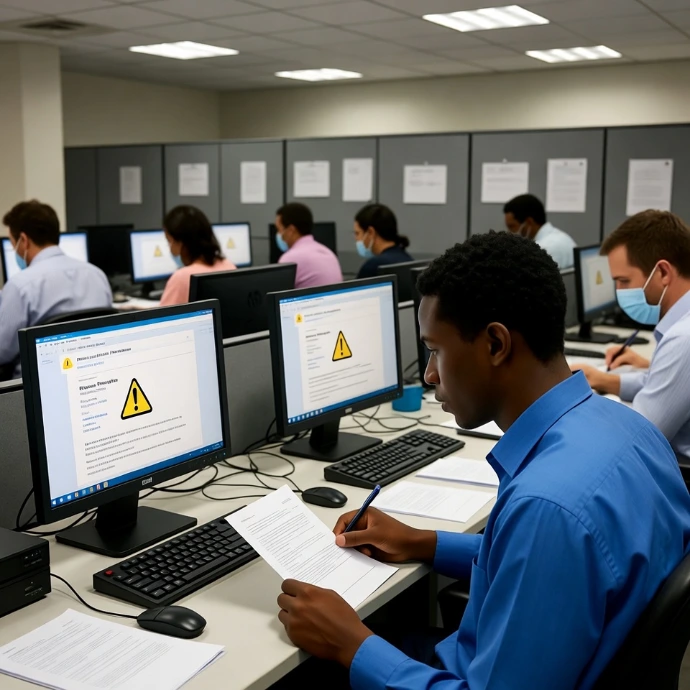
Phishing Simulation
Test your defense with Simulated Phishing Attacks to measure employee alertness in real-time.
Updated Curriculum
Content stays ahead of the curve, covering new threats like AI Deepfakes, Social Engineering, and Mobile Security.
Actionable Analytics
Individual behavioral analysis reports to identify high-risk areas and improve precisely where needed.
Why Cybernetics+?
Beyond Standard Training – The Cybernetics+ Standard
General Training | What You Get with Cybernetics+ |
Academic, complex content | Practical, digestible, and fun content |
One-time session | Continuous learning & follow-ups |
No clear measurement | Comprehensive Organizational Risk Dashboard |
Outdated scenarios | Updated with the latest threats |
Comprehensive Security Coverage
✽ What We Offer (Our Modules : Sample Curriculum)
Password Hygiene
Best practices for strong passwords and securing accounts with 2FA.
Email Security
How to detect Phishing attempts and malicious links.
Social Engineering
Recognizing the psychological tricks hackers use to manipulate people.
Remote Work Security
Safe practices for working off-site and using Public Wi-Fi.
Data Protection
Personal Data Protection Act (PDPA/GDPR) compliance for employees.